
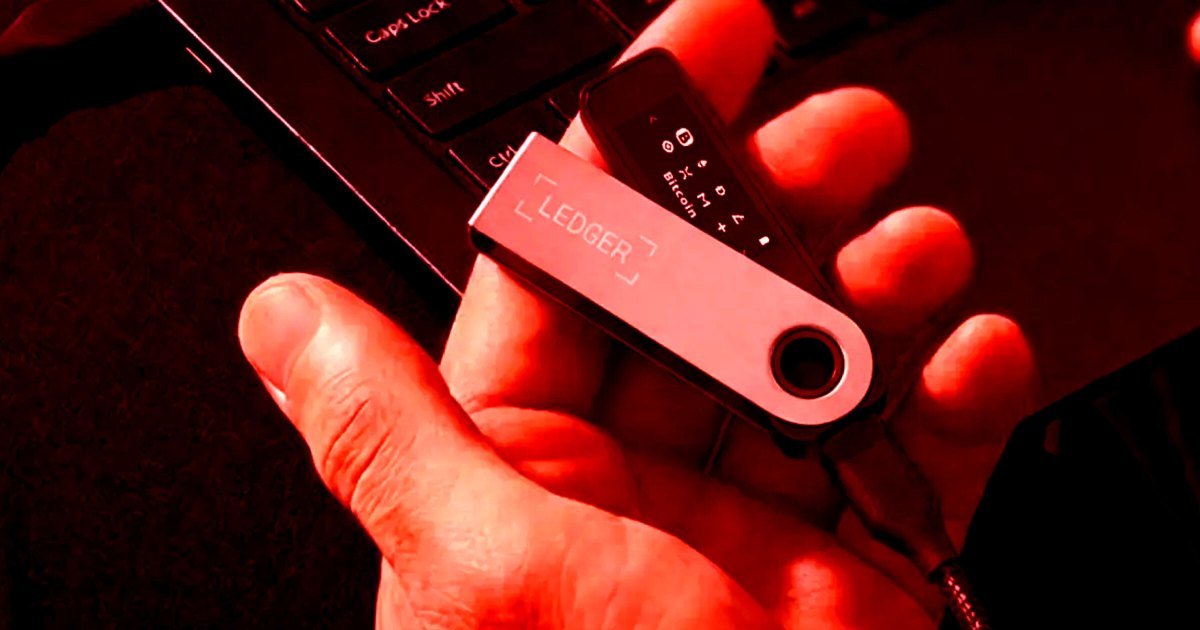
When your company’s bread-and-butter is selling crypto devices advertised as having “industry leading” security, you better keep a close eye on your supply chain.
That’s a hard lesson learned by Ledger, a company specializing in secure blockchain wallets, after news broke that some of its devices had been infiltrated by a mysterious “hardware implant.” According to Bleeping Computer, the malicious implant was designed to monitor inputs made onto each wallet via on-board buttons, along with changes in output on the devices’ e-ink screens.
By monitoring this data, the hardware implant could reportedly identify the use of a seed phrase — a sequence of words used to generate static wallet addresses on the blockchain — which it would then transmit to hackers using an eSIM.
As a result of the implants, a number of Ledger users had their crypto wallets drained, prompting an investigation by the company. After probing a number of devices, Ledger concluded that the compromised wallets originated from an electronics reseller out of Malaysia named CryptoBilis.
